Phishing via HTML Injection in Gemini's Chart Renderer
Using CVE-2025-25304 to take over a Vega iframe in Google’s Gemini web interface, inject JavaScript into a sandboxed iframe, then phish through shared conversation links.
Using CVE-2025-25304 to take over a Vega iframe in Google’s Gemini web interface, inject JavaScript into a sandboxed iframe, then phish through shared conversation links.
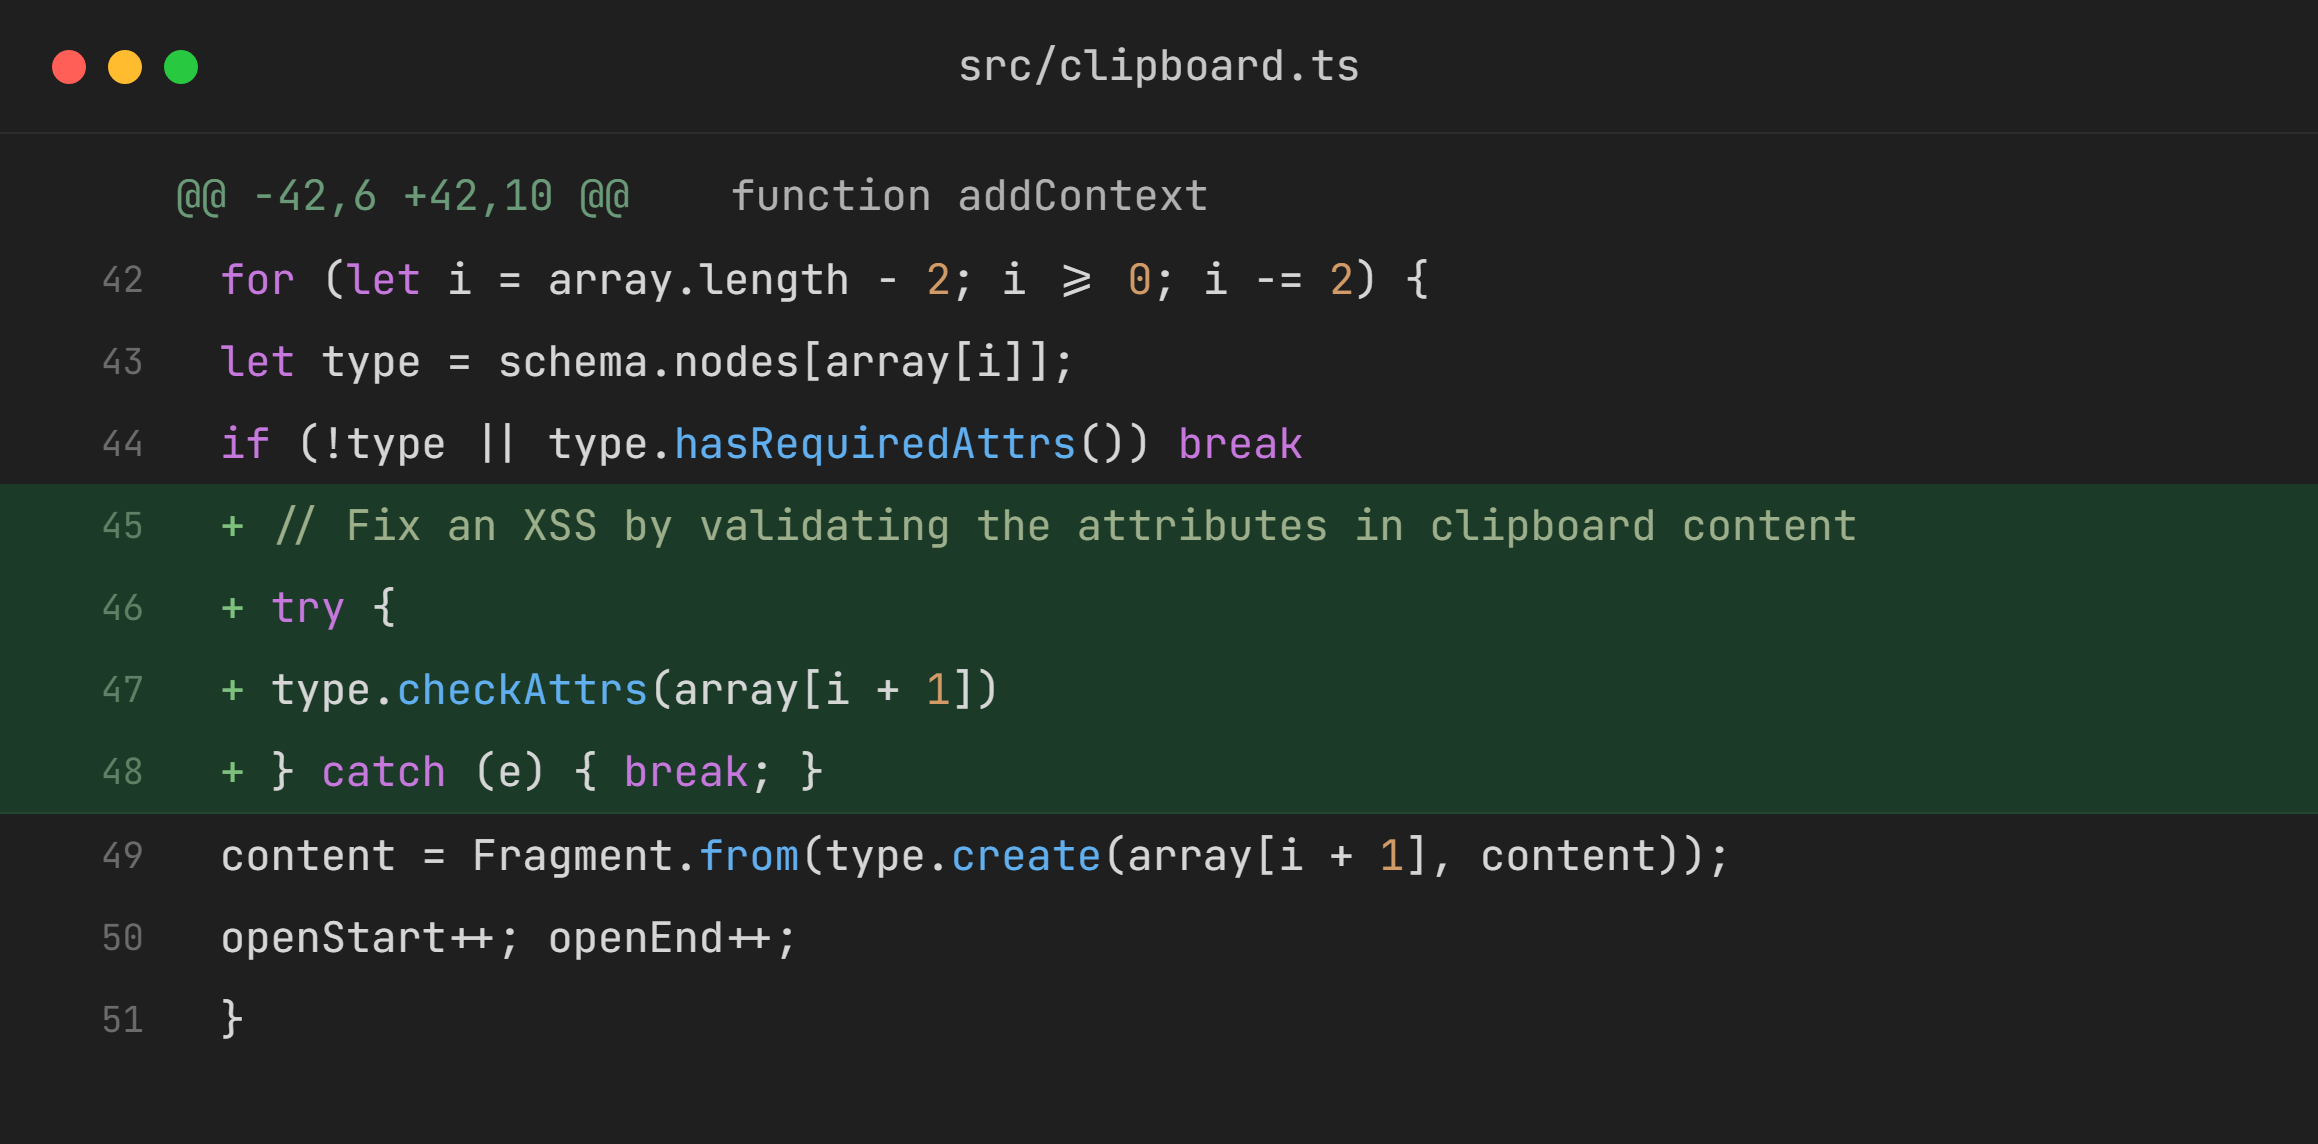
An analysis of ProseMirror-view 1.42.3’s patch to understand how a clipboard paste containing a malicious payload could achieve XSS (GHSA-c8x8-7fp4-3x9w).