Phishing via HTML Injection in Gemini's Chart Renderer
Using CVE-2025-25304 to take over a Vega iframe in Google’s Gemini web interface, inject JavaScript into a sandboxed iframe, then phish through shared conversation links.
Using CVE-2025-25304 to take over a Vega iframe in Google’s Gemini web interface, inject JavaScript into a sandboxed iframe, then phish through shared conversation links.
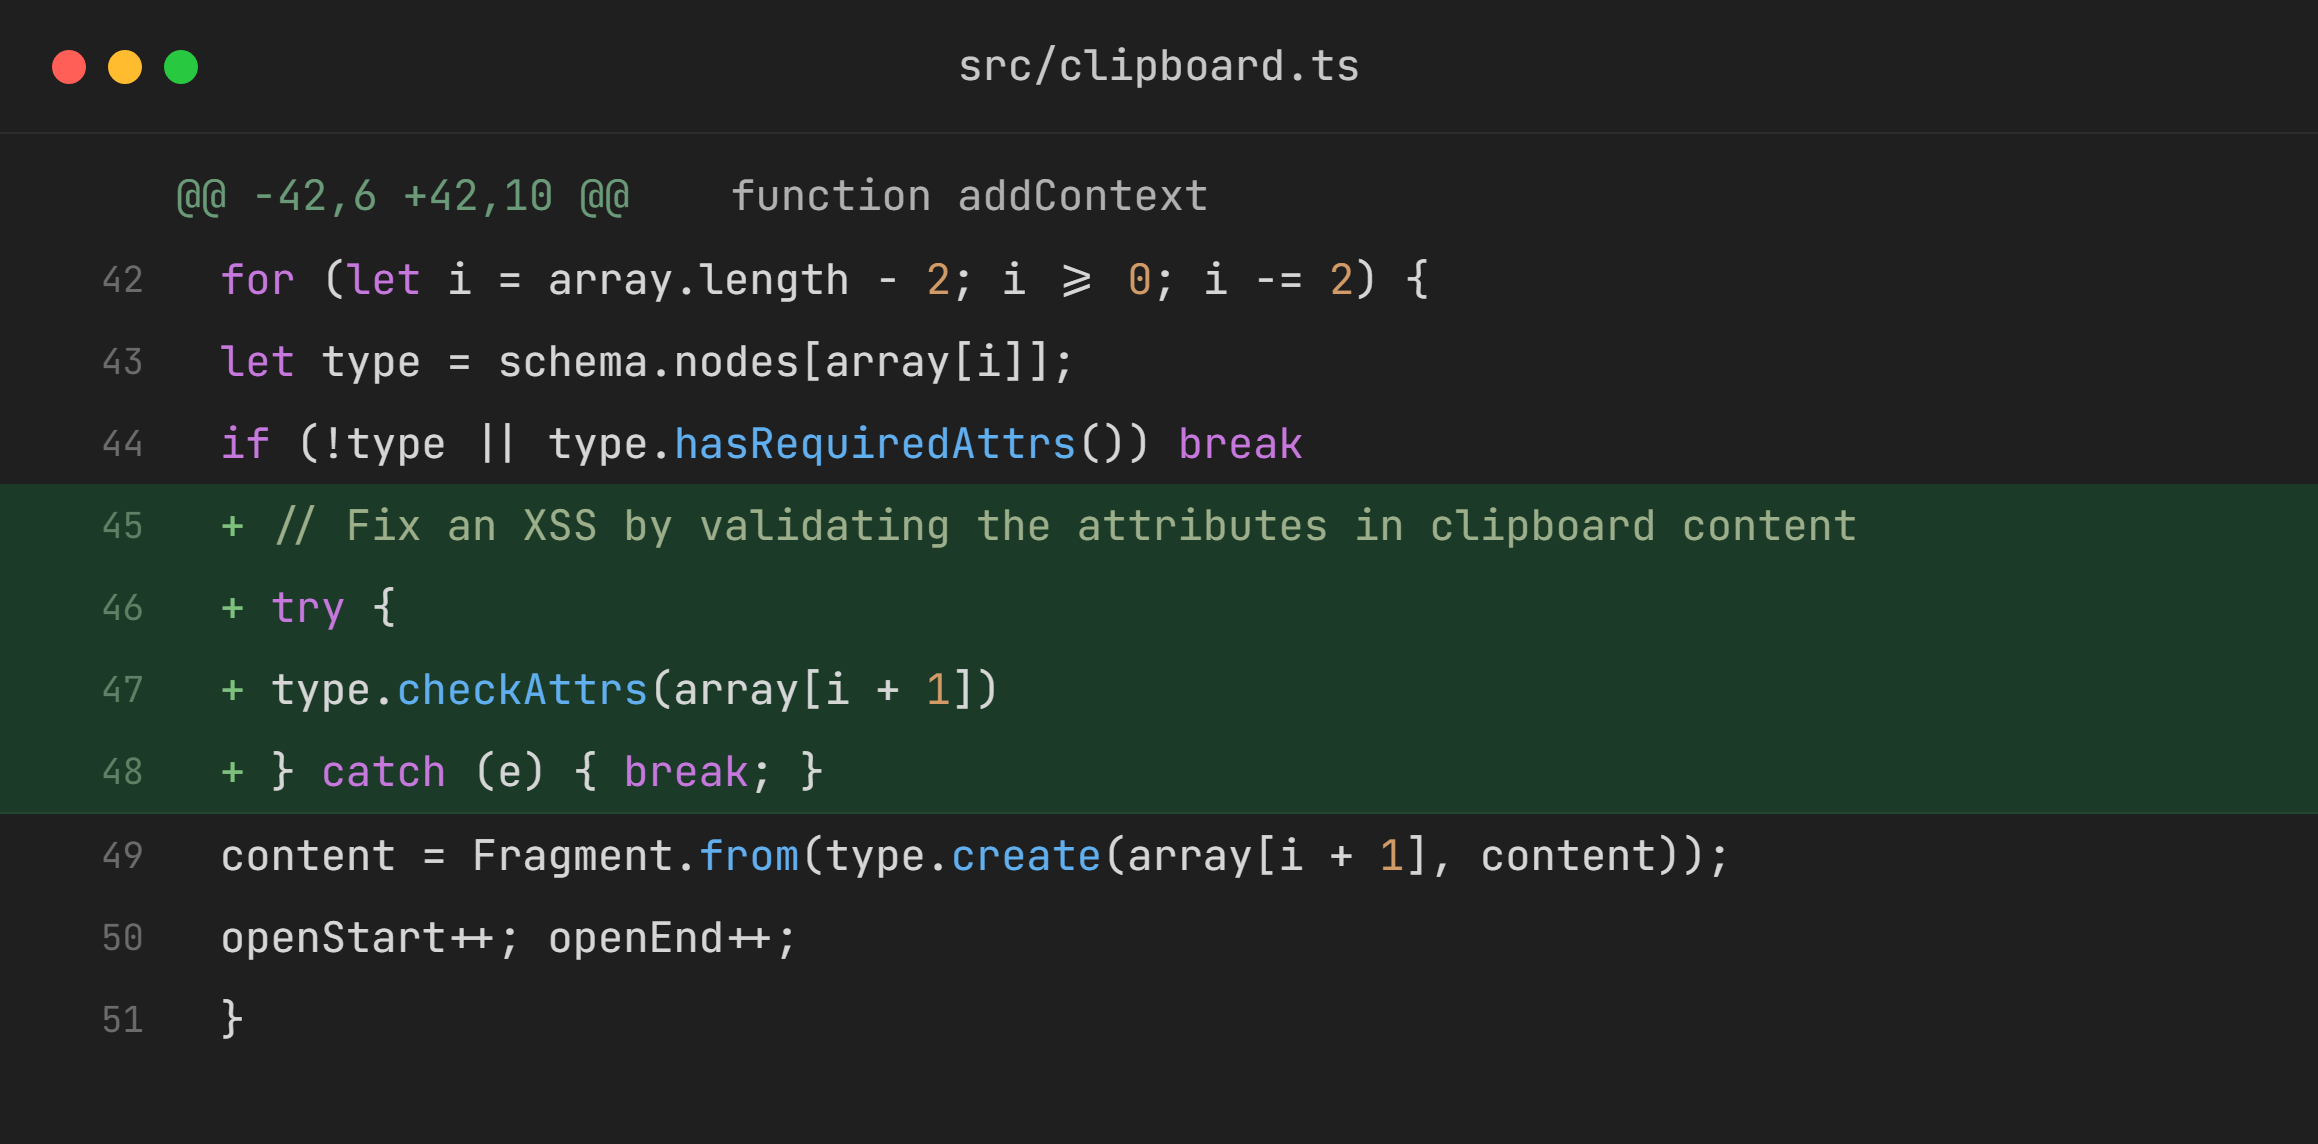
An analysis of ProseMirror-view 1.42.3’s patch to understand how a clipboard paste containing a malicious payload could achieve XSS (GHSA-c8x8-7fp4-3x9w).
A detailed walkthrough on how I chained two different tricks (iframe srcdoc and a CSP bypass) to achieve XSS. Then an explanation of how Google patched the vulnerable code.
Creative writing is on life support because of AI misuse.
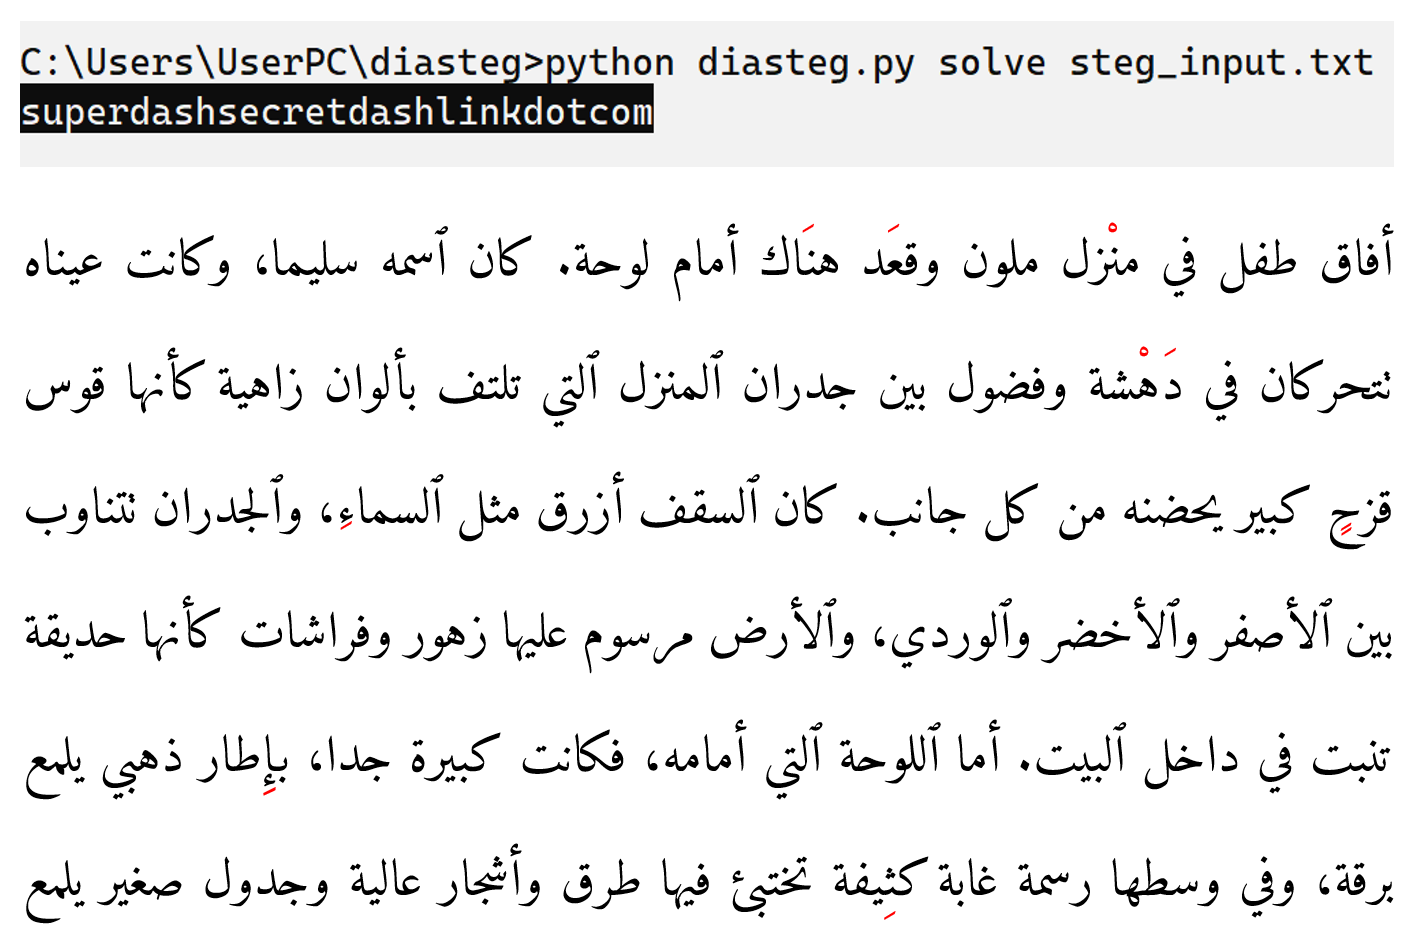
What magic happens when you XOR two Arabic letters together? English!